 s3-presigned-url-proxyv2026.07.27.0833
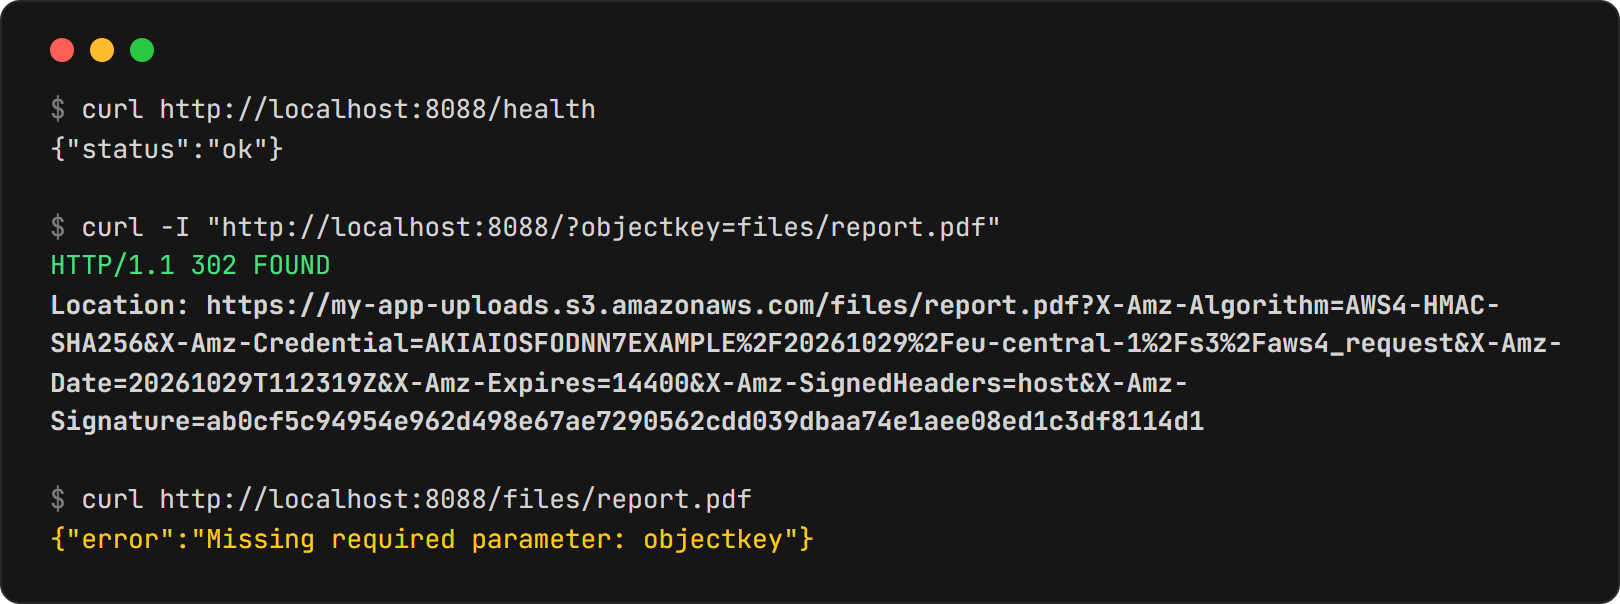
Your app builds a plain URL with the object key; the proxy signs a time-limited S3 link and 302-redirects to it, so the browser downloads straight from S3. One container, no AWS SDK wiring in every service. For local development.
$ cp .env.example .env       # AWS_BUCKET + credentials
$ docker-compose up -d
$ curl http://localhost:8087/health
{"status":"ok"}
The key comes in as a query parameter; a pre-signed GET URL goes out in the Location header, valid for four hours by default.
Responses
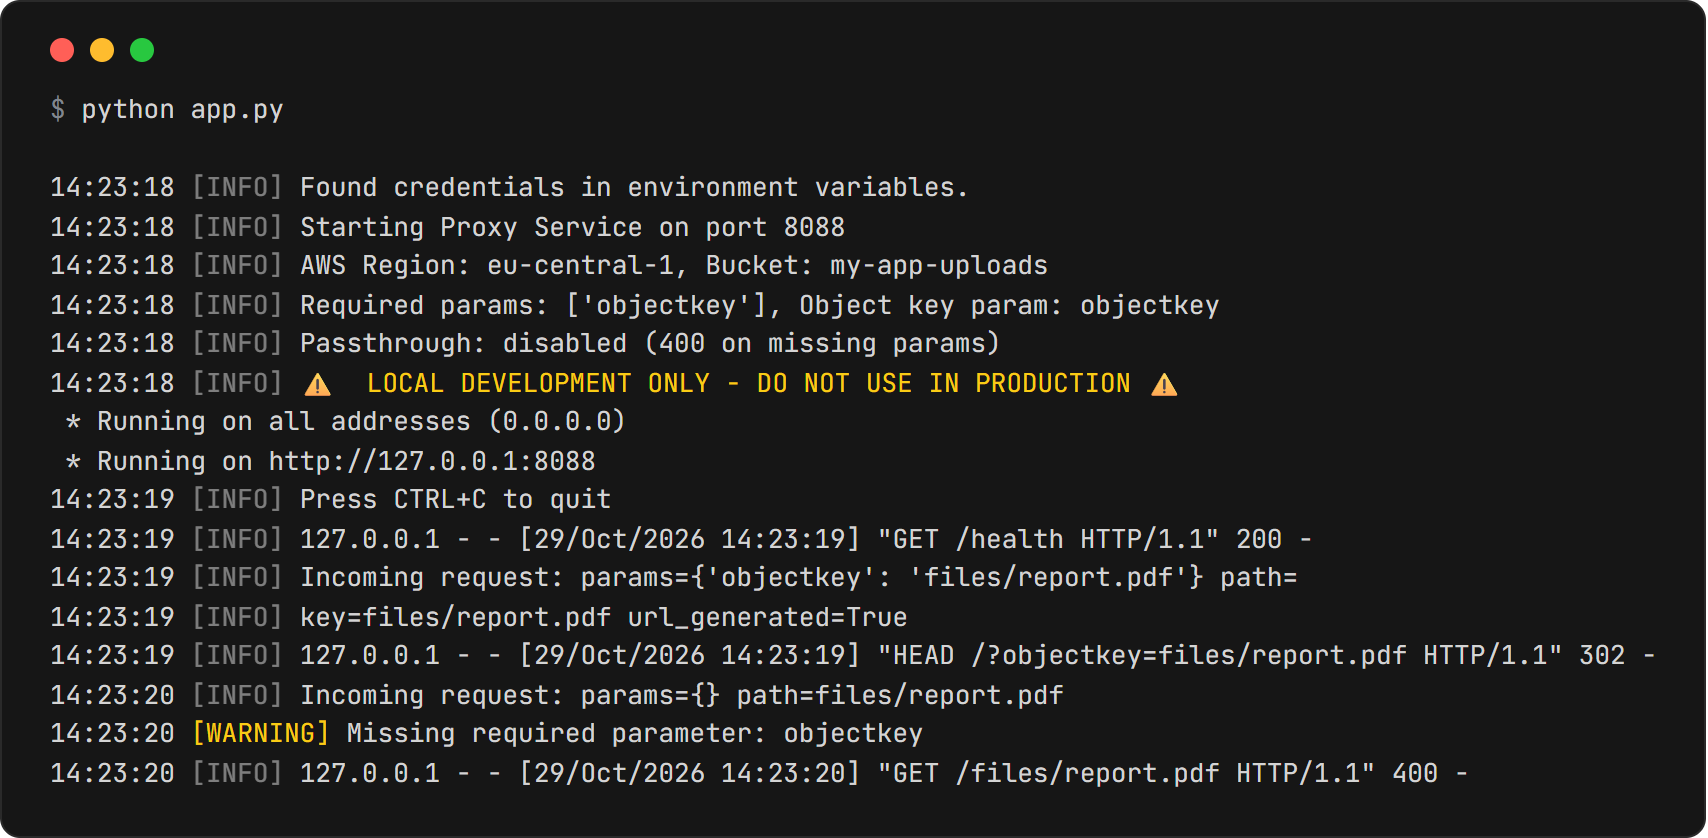
Methods GET, POST, PUT, PATCH and DELETE, on / or any path; the path is ignored. A request with only some of the required parameters still gets a 400, so a typo shows up instead of a broken link.
Configuration
The container
The compose file runs it on a read-only filesystem with no new privileges, a quarter of a CPU and 256 MB, and a health check every 30 seconds. Images for amd64 and arm64 are on Docker Hub, released on every push.
read_only: true
tmpfs: [/tmp, /run]
security_opt: [no-new-privileges:true]
cpus: 0.25
mem_limit: 256m
healthcheck: every 30s, 3 retries
ports: ["8087:8088"]   # host 8087, container 8088
Get it
The published image
Docker Hub$ docker run -d -p 8087:8088 --env-file .env ugurcandede/s3-presigned-url-proxy:latestCredentials need s3:GetObject on the bucket. Don’t expose it to the internet: there is no authentication.